Security

Advanced Threat
Detection & Response

Detect hidden malware, accelerate forensic investigations, and guarantee clean, evidence-based recoveries with Druva Threat Insights.

On the Offensive

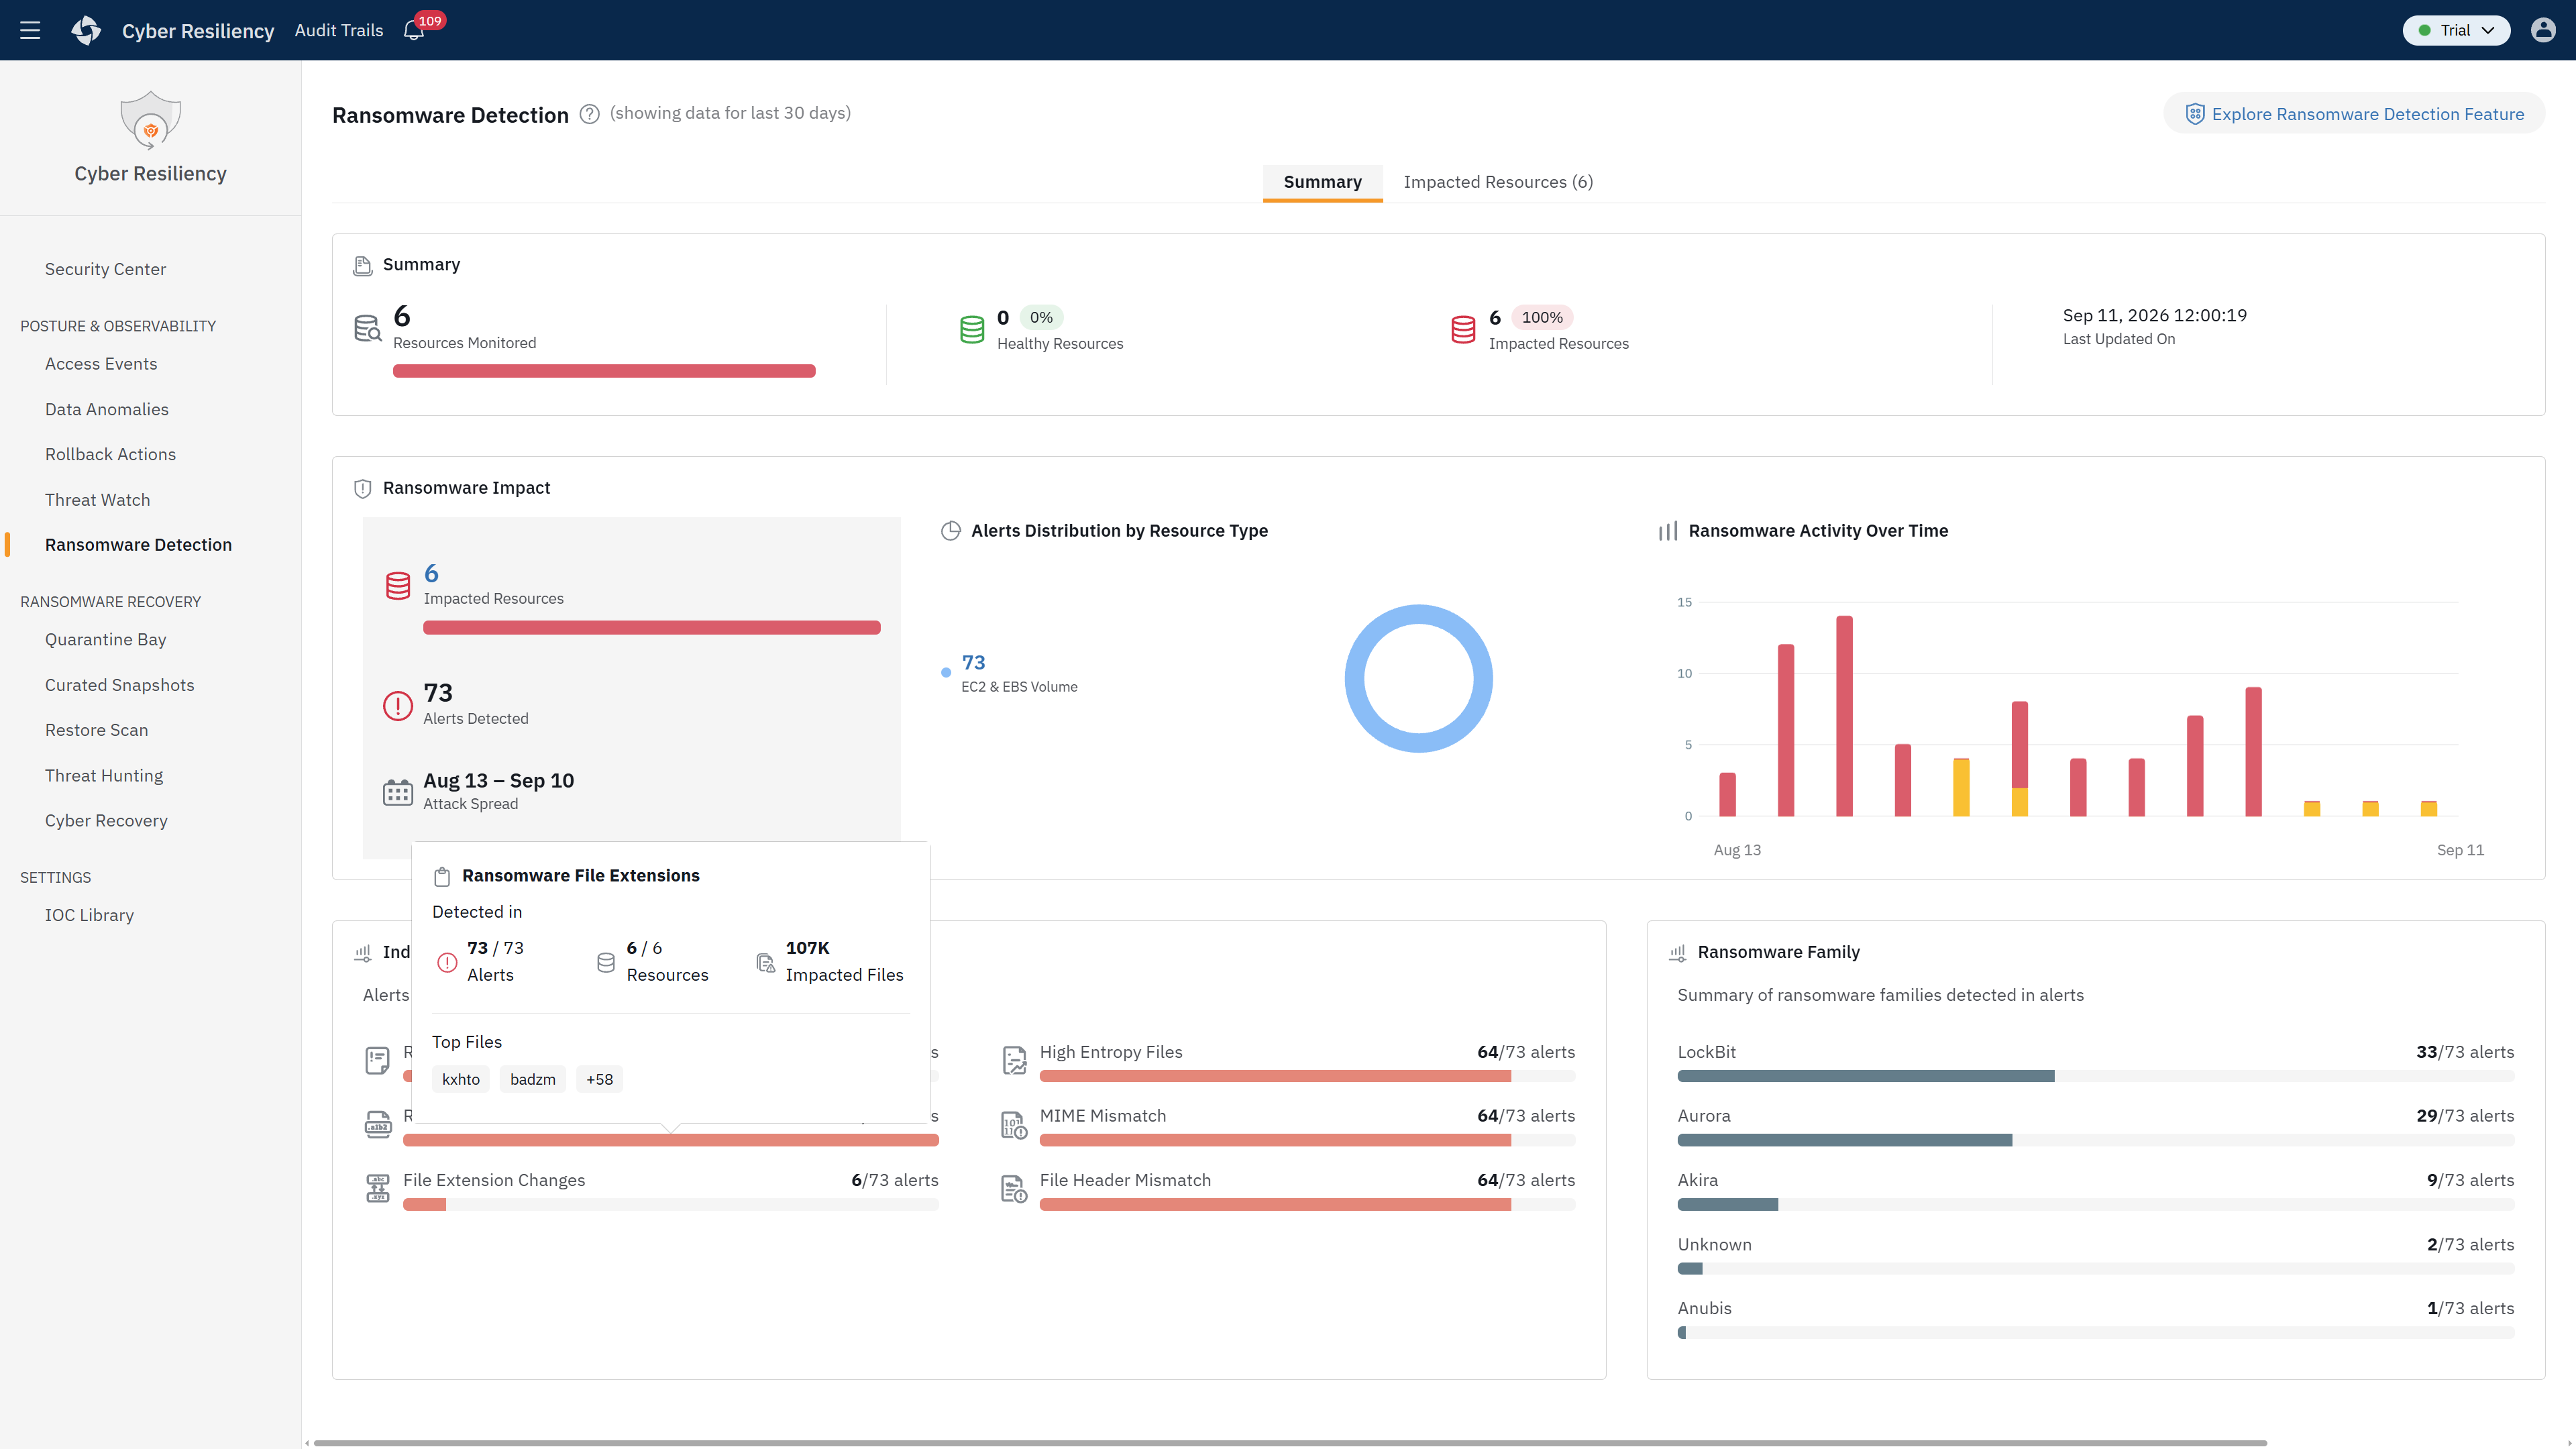
Use backup data for more than recovery! Druva turns backup telemetry into actionable insights to uncover known and unknown ransomware, understand compromise, and validate clean restore points with confidence.

Druva’s AI-powered detection and forensic validation engine identifies and confirms ransomware threats, assesses impact and blast radius,  and guides evidence-based recovery.

insider threat icon

Advanced Behavioral Detection

Detect known and unknown ransomware threats by continuously analyzing backup snapshots for suspicious behaviors, such as ransom note proliferation, novel file extensions, mass file renaming, and more.

compliance icon

In-Platform Validation
 

Through built-in structural, data, and entropy analysis, we verify suspected encryption and provide rapid, definitive proof of ransomware while reducing false-positive alerts by ~98.

recovery icon

Streamlined Recovery Intelligence

Gain clarity on the scope of attacks and impacted data to confidently pinpoint clean recovery points, minimize downtime, and prevent the risk of reinfection.

Automated, continuous scanning of backup snapshots with retrospective rescans when new IoCs emerge. Powered by Recovery Intelligence, quickly understand blast radius, identify clean restore points, and reduce reinfection risk during recovery.

malware detection icon

Continuous Backup Scanning

Scans multiple times daily on changed snapshots and automatically rescan the last 30 days when new threats emerge, optimizing speed and relevance.

cloud check icon

Zero-Infrastructure Footprint

Get powerful threat monitoring without requiring agents or dedicated scanning nodes, simplifying deployment and reducing operational overhead.

no ransomware icon

Rapid, Context-Aware Response

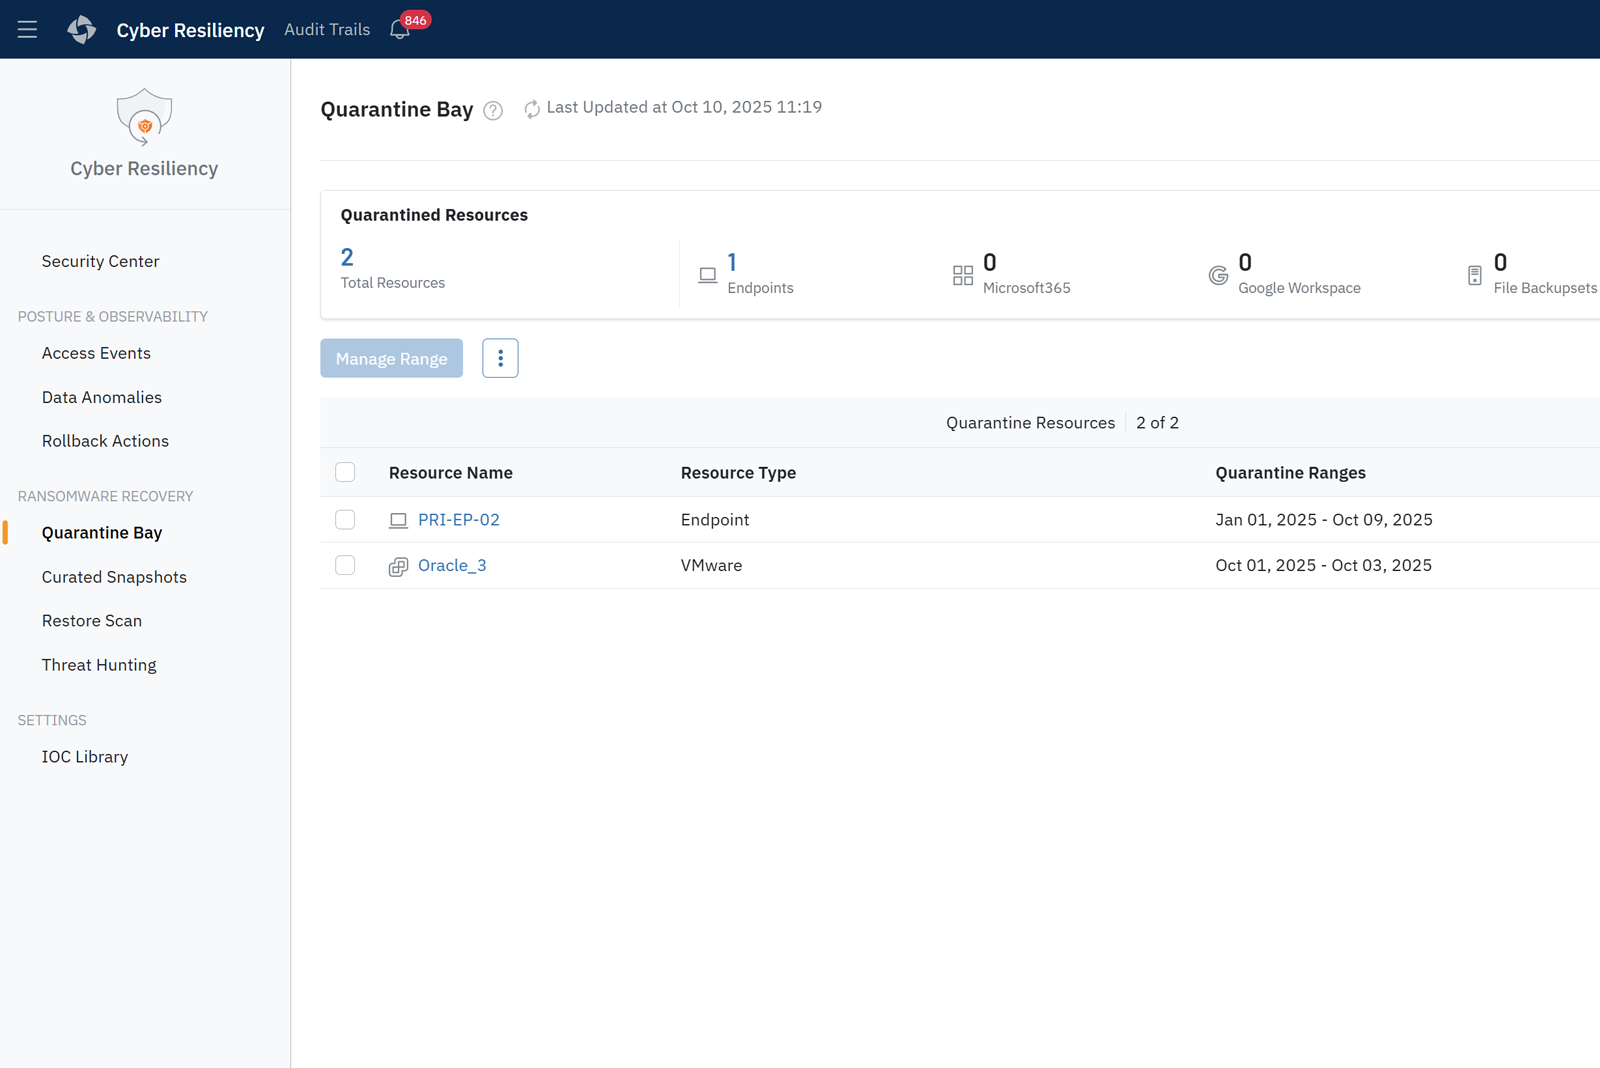
Infected snapshots are automatically quarantined, and high-priority alerts integrate with SIEM/SOAR for rapid triage and automated response playbooks.

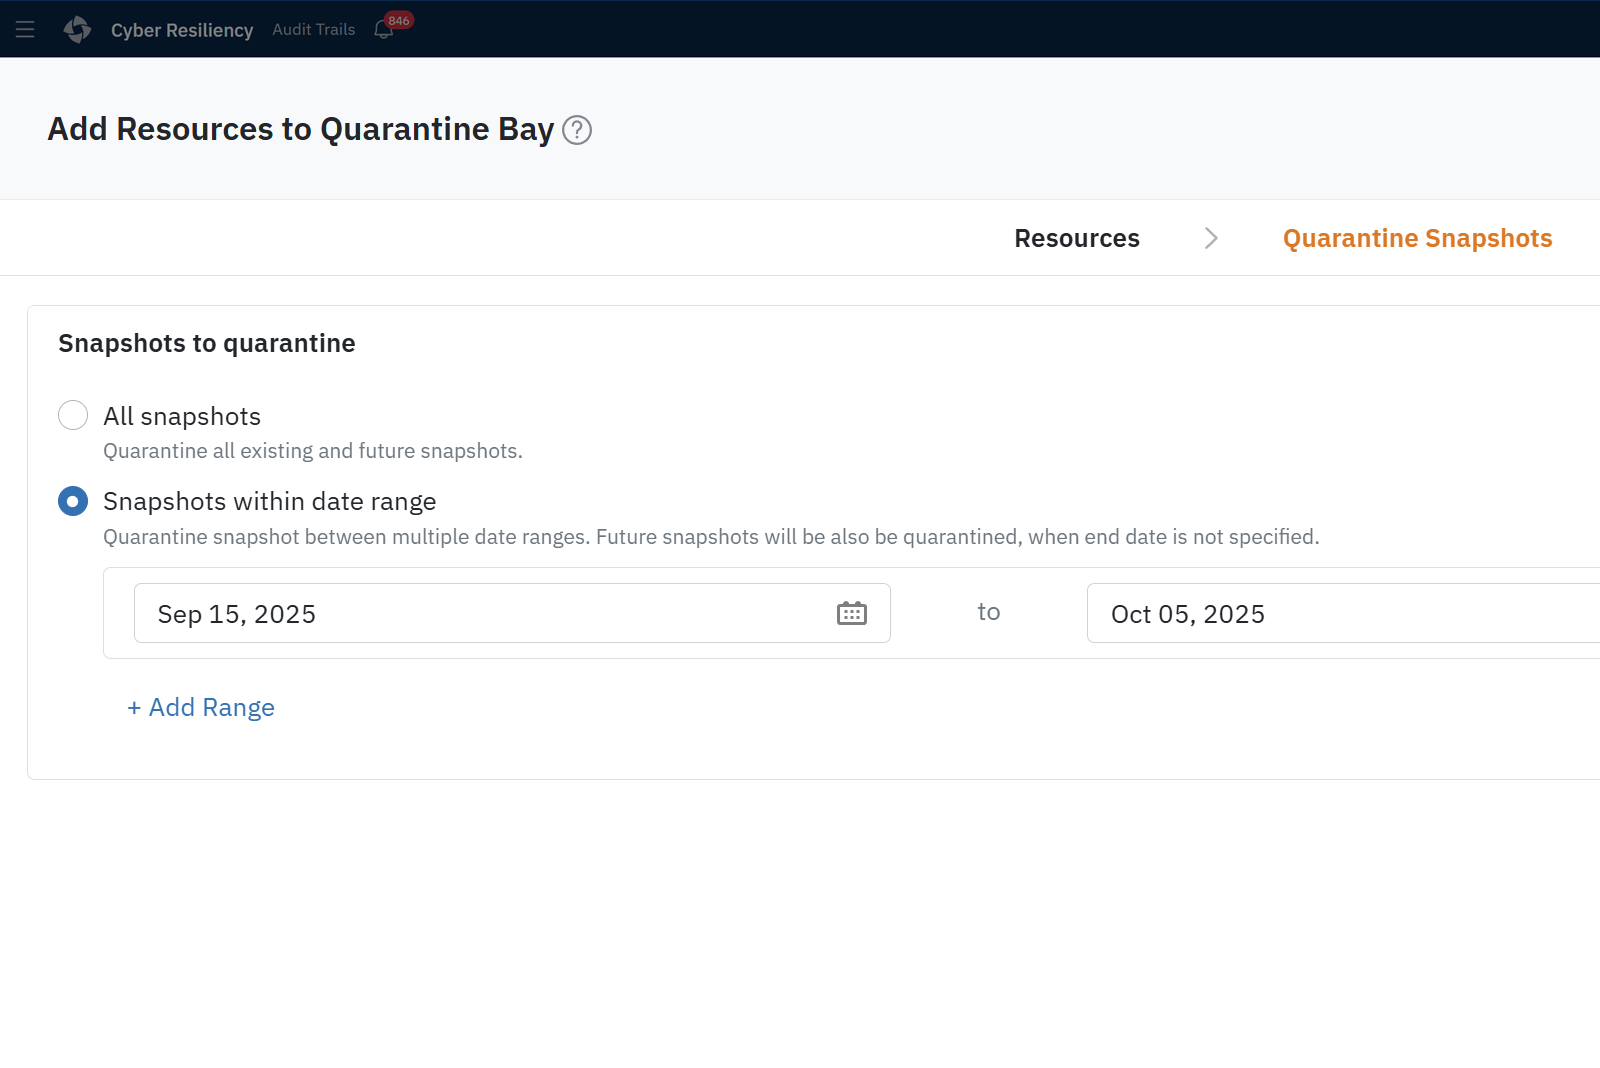
Search metadata to locate IoCs and establish scope / timeline of an attack. Quarantine infected files and snapshots and defensibly delete to remove compromised data from backups and primary environments, ensuring recovery proceeds from clean data.

compliance alert icon

Powerful Historical Investigation

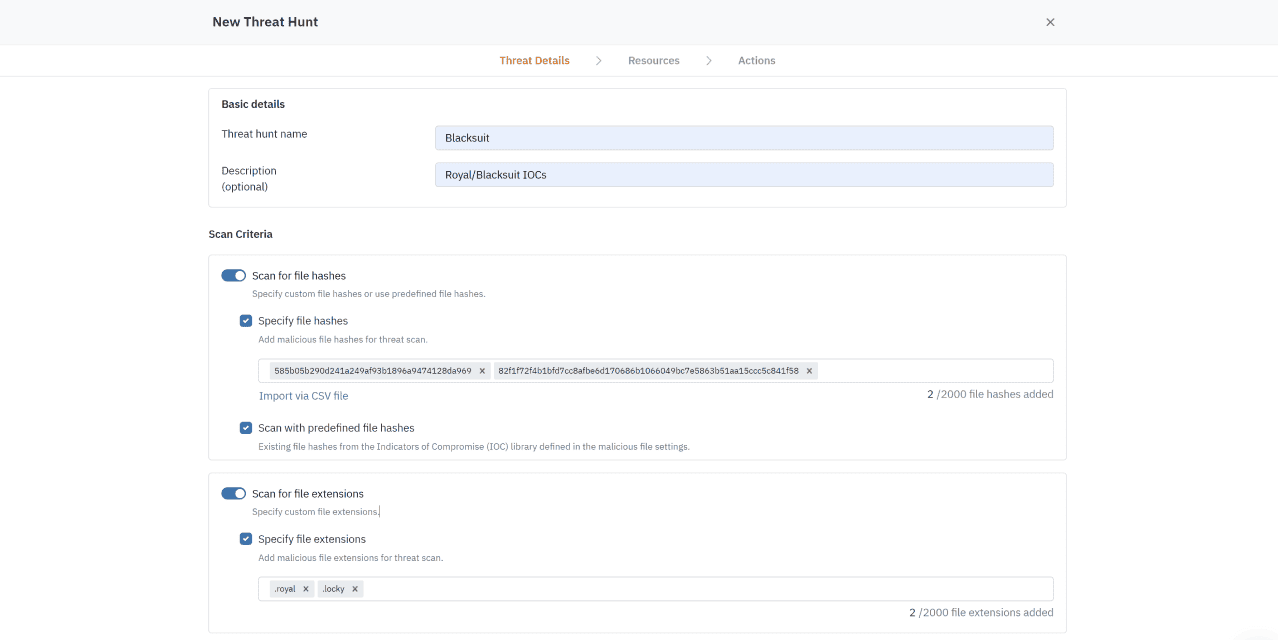
Search indexed backup metadata (hashes, file attributes) across historical backups to understand the scope and timeline of an attack.

autonomous protection icon

Data Recovery Confidence

Support optional validation (e.g., sandboxing) prior to recovery and allows for defensible deletion of compromised data, ensuring a clean restore point.

data intelligence icon

Comprehensive Threat Intelligence

Leverages aggregated data from CISA, Mandiant, Google, and Druva ReconX Labs, plus allows for custom, customer-driven IoC feeds.

star-icon
Related Content

How It Works

Threat Insights, when combined with robust backup strategies, creates a powerful defense against modern cyber threats. It's time to move beyond simply protecting your data to actively hunting down those who threaten it.

Leverage signature scanning,  heuristic checks, and deep structural forensics to detect and confirm the presence and impact of ransomware. Then, restore only verified clean snapshots to resume business operations with absolute confidence.

Search for Indicators of Compromise (IOCs) based on metadata across backups to accelerate investigation and response. Discover infections lying dormant in your backups. Take containment, remediation, and recovery actions based on this information.

Isolate infected snapshots, either manually or automatically, across workloads. This prevents reinfection, limits attack scope, and ensures clean recovery points.

Delete infected files from backups. Receive convenient reports for auditors and cyber insurance, ensuring compliance with security processes.
In-Platform Intelligence, Powered by Druva ReconX Labs

Our curated IOC library and proprietary AI threat pipeline power Druva Threat Insights to enhance ransomware detection, quantify impact, and drive precise recovery — all natively within our platform.

Related Capabilities

ransomware

Accelerated Ransomware Recovery

Shorten incident response time and cyberattack recovery with automated security workflows and integrations.

security

Security Posture & Observability

Get real-time insights into your data security and how your environment has changed over time. Fortify your backups with these enhanced security insights.

security sytems

Managed Data Detection & Response

24x7 security monitoring of backups, expert analysis, and support for threat monitoring, investigation, response, and cyber recovery.

anomaly detection icon

Anomaly Detection

Get cloud indexing, comprehensive threat detection for real-time protection, SLA adherence, and robust security with high efficiency.

security

Restore Scans

Proactively scan backup data for malware and known threats before restoration, ensuring clean data recovery and preventing reinfection of systems.

recovery intelligence icon

Recovery Intelligence

Ensure fast, secure data restoration with automated intelligence, anomaly detection, and forensic support for precise and efficient cyber recovery.
“We’ve slashed the time for recovery from up to eight hours down to a few minutes with Druva — about 90% faster.”

Tom Ferrucci CIO, Hope Global

Trusted by the world’s leading organizations
Related Resources
Blog

Explore peacetime and wartime applications. Get a guide to remediating threats to your backup environment, and prevent downtime.
Demo

Get a step-by-step guide to Threat Hunting and Threat Watch. Defeat malware and bounce back to clean data with ease.
Whitepaper

Gain confidence in your IRR workflow with access to a single source of truth and CloudOps experts to assist in remediation and recovery.

Get started now.

See for yourself why Druva is the leader in data security.